When cybersecurity is treated as a purely technical concern, with no genuine governance or oversight behind it.
No Board-Level Oversight: Cybersecurity is treated as a technical responsibility with no board-level oversight.
How we can help
Digital trust and resilience built on genuine governance, not just tools.
Cybersecurity is often approached as a set of technical controls, when the organisations most resilient to digital risk are the ones that treat it as a governance discipline, with clear accountability, policy and oversight, not a checklist of tools purchased once and left unreviewed.
Tools alone do not create resilience. Without governing policy, board-level oversight and regularly tested incident response plans, technical controls can leave gaps that are only discovered once an incident has already occurred.
At Concinnity, we strengthen trust, resilience and governance across digital operations, building the accountability and oversight structures that make cybersecurity sustainable, not just technically present.
We help organisations treat cybersecurity as a governance discipline, building the accountability, policy and oversight structures that make digital resilience sustainable.
The result is cybersecurity that is genuinely governed, not simply technically present, with resilience tested before it is needed.
Design the governance structures, accountability and oversight required to manage cybersecurity as a leadership responsibility, not just a technical one.
Assess the organisation's digital risk exposure, establishing an honest, evidence-based view of where vulnerabilities actually sit.
Develop the policies and standards required to govern how security tools and controls are actually used across the organisation.
Establish the reporting lines, oversight mechanisms and decision rights that give boards and leadership genuine visibility of digital risk.
Design and test incident response plans so the organisation's resilience holds when it is actually needed, not just on paper.
The common thread: security tools are in place, but the governance required to make them genuinely effective is not.
No Board-Level Oversight: Cybersecurity is treated as a technical responsibility with no board-level oversight.
Security tools have been purchased but there is no governing policy behind their use.
A digital risk assessment has not been conducted in years, if ever.
Incident response plans exist on paper but have never been tested.
Leadership cannot confidently answer basic questions about the organisation's digital risk exposure.
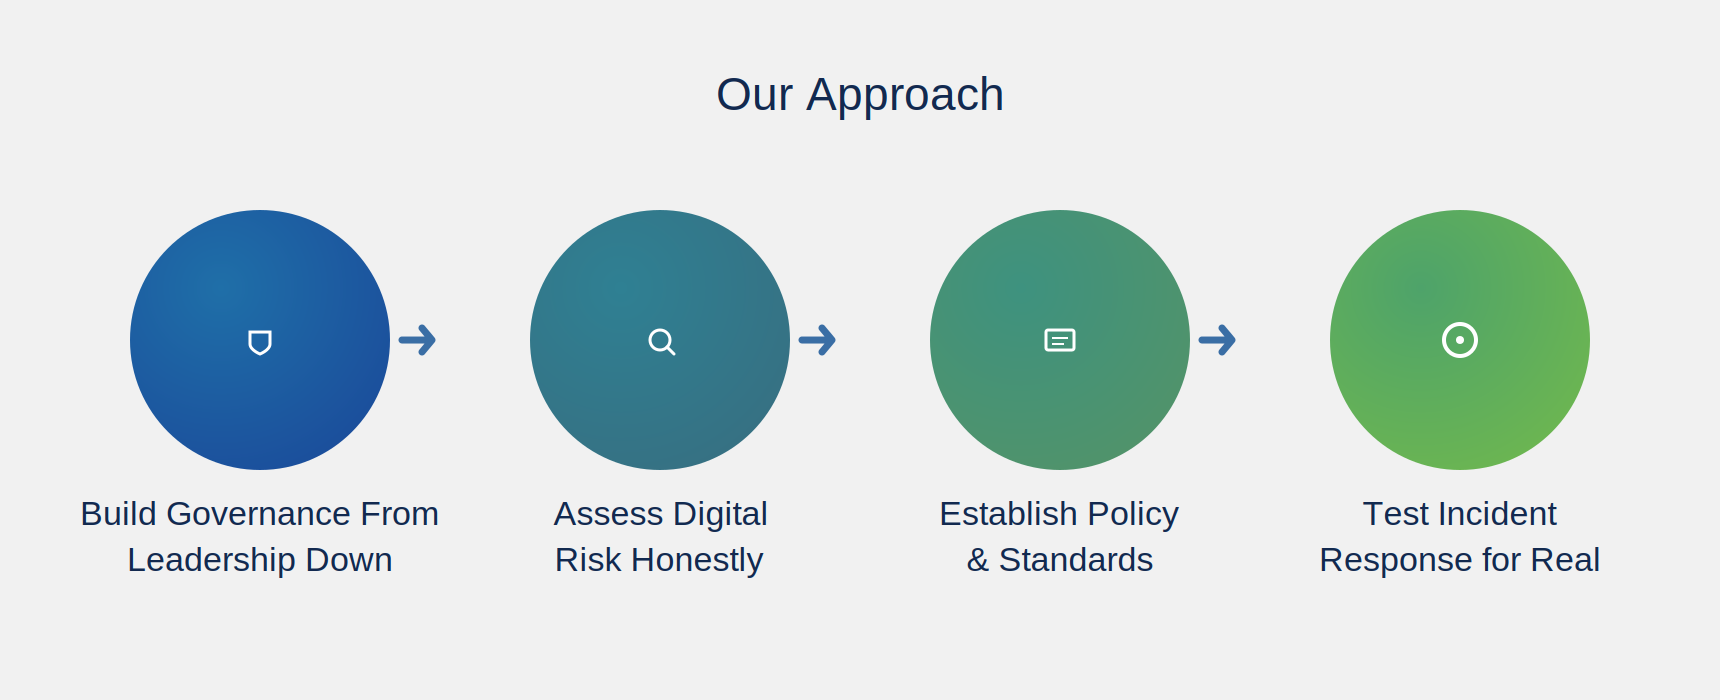
We build cybersecurity governance from the leadership level down, establishing accountability and oversight before recommending specific technical controls.
We assess digital risk honestly, giving leadership an evidence-based view of the organisation's actual exposure rather than an assumed level of security.
From there, we establish the policies and standards that govern how tools and controls are actually used, ensuring technical investment operates within a coherent governance structure.
Risk assessments and incident response plans are tested for real-world readiness, not simply documented, so resilience holds when it is actually needed.
The result is digital trust and resilience built on genuine governance, tested and ready rather than simply documented and assumed.